
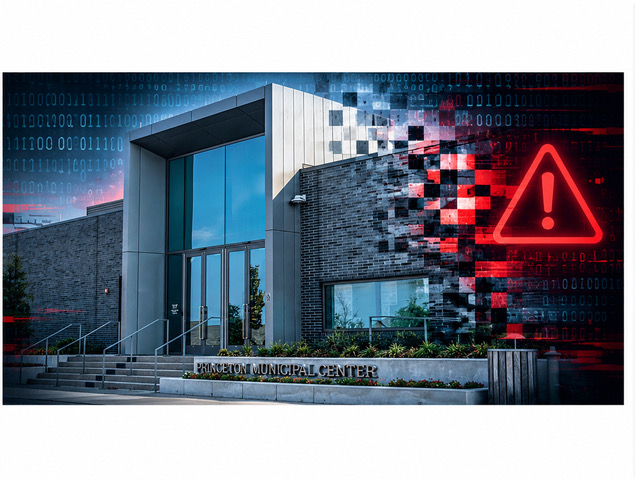
Two weeks after first reporting a potential data breach, the city of Princeton has confirmed that confidential information and personally identifiable information was downloaded from municipal computer systems.
On Sept. 18, Princeton said it was investigating what was called a “cybersecurity incident involving potential unauthorized access to certain city systems and data.”
Four days later, an update referred to an “alleged cybersecurity incident” and said two independent reviews had been conducted by cybersecurity experts.
“Based on the information currently available, neither review has identified evidence indicating unauthorized access to city systems, a confirmed data breach or unauthorized data exfiltration,” the Sept. 22 notice said.
But in the most recent release on Oct. 5, the city said it had found information was indeed exfiltrated from city systems.
“The city is working with cybersecurity professionals to determine the full scope of the incident, including what information was involved and which individuals may be affected,” the notice said.
It said the continuing forensic investigation identified additional information requiring further review.
“At this time, the city is still actively investigating the incident and working to determine the full scope of any systems or individuals that may have been affected,” said Mayor Eugene Escobar Jr. “All impacted parties will be contacted directly with appropriate guidance.”
While the investigation remained ongoing, essential city services continued to operate normally.
After the initial report, the Princeton City Council added an emergency item about the potential breach to the agenda of its Sept. 21 special meeting but said there was nothing else to report at that time.
On Sept. 28, a resident told councilmembers he thought unauthorized purchases had been made with a personal credit card he had on file with his city account.
The man, who identified himself as a technology specialist, said information purported to come from the hack, had been posted online by an organization known to make ransom demands for purloined data.
“They don’t break things, they just take the information and leave,” he said after the meeting.
When a city in Texas confirms a data breach affecting 250 or more residents, it must complete and submit two separate mandatory filings to state authorities.
The city must file an electronic Data Breach Report with the Texas Attorney General as soon as practicable, and no later than 30 days after determining the breach occurred.
It must contain a detailed description of the incident, the exact number of affected residents, measures taken (and planned) for remediation and whether law enforcement is actively investigating. Those reports are then relayed online.
Because a city is a local government entity, it is also subject to Texas Government Code § 2054.603 (enacted via SB 271), which mandates parallel security incident reporting to the Texas Department of Information Resources (DIR). However, those reports are closed to the public.
Stay informed, and support your local community newspaper, subscribe to The Princeton Herald
0 Comments